Security & Compliance
Close exposure before it becomes risk.
Years of quick access grants left an org no one can fully explain — with an audit and an AI rollout both waiting on it. Hubbl maps the whole access model in about two minutes, ranks the real exposure, and hands you the fixes — so you can prove least privilege, stay audit-ready, and secure the foundation before agents run on top of it.
You can't secure — or certify — an access model no one can see.
Every admin, integration, and "just give them access for now" adds another door to your org. Over years, no one can say who can reach what, which grants are still needed, or where sensitive data is actually exposed. That blind spot is a failed audit and a breach waiting to happen — and the single biggest risk when you hand an agent the keys. Hubbl turns the access model into something you can see, rank, fix, and prove.
The access model, finally visible.
Hubbl maps every profile, permission set, sharing rule, role, and integration user into one picture — and traces the real paths to sensitive records, including the inherited access no permission screen shows.
- Permission & exposure heatmap
Over-permissioning and exposed PII, at a glance. - Access-path analysis
Every route to a sensitive object, direct and inherited. - "Who can see this?"
Answer it for any record in seconds.
Fix the doors that matter first.
A raw findings list isn't a plan. Hubbl ranks exposure by severity and blast radius and attaches a ready-to-run fix prompt to each item — so you close the real risk instead of chasing every flag.
- Ranked by risk
Severity and blast radius, highest first. - Stale & integration users
Dormant admins and high-privilege service accounts, surfaced. - Fix prompts included
Ready to run in Claude or Salesforce Vibes.
Walk into the audit with the evidence already in hand.
Compliance isn't a one-time scramble. Hubbl documents least privilege, tracks exposure over time, and keeps a record of what changed and when — so you demonstrate control instead of reconstructing it the week before the auditor arrives.
- Least-privilege evidence
The delta between granted and actually needed, documented. - Drift history
An audit-ready record of every access change. - Continuous monitoring
New exposure flagged in days, not at the annual review.
Agents inherit your access model. Lock it down first.
An agent is only as safe as the org it runs in. Every over-broad permission and hidden path becomes something an agent can act on — at machine speed. Hubbl makes a secure foundation a prerequisite for AI, not an afterthought.
- Agent-safe permissions
No over-broad access for agents to inherit. - Contained blast radius
Know exactly what an agent could reach. - Audit trail for AI
Prove the foundation was secure before go-live.
Every solution runs the same play.
No matter the role or the goal, Hubbl follows one motion — turn the lights on, understand and act, then stay clean and get AI-ready.
See the whole org
A credential-free X-ray in about two minutes — inventory, security exposure, and process reality no admin could map by hand.
Fix what matters first
A ranked backlog with the fix attached to every item — close out tech debt at the speed of AI instead of letting it pile up.
Keep it healthy
Continuous monitoring holds the line as the org evolves — and keeps the foundation ready for agents and Agentforce.
From an unexplainable access model to security you can prove.
You stop guessing who can reach what. Exposure is ranked and closed, least privilege is documented, and the audit trail writes itself as the org changes — so security is something you demonstrate on demand, and AI runs on a foundation you've already locked down.
- See who can reach any record - in seconds, not days of digging.
- Close real exposure first - ranked fixes with ready-to-run prompts.
- Prove least privilege - to any auditor — with history to back it.
Built for everyone accountable for access.
You own security & IT
"I'm accountable for a surface I can't fully see."
Surface exposure, prove least privilege, and shrink the attack surface before AI expands it.
You're facing an audit
"I rebuild the evidence from scratch every cycle."
Walk in with the access model documented and every change tracked over time.
You're rolling out agents
"Leadership wants Agentforce on a foundation I'm not sure of."
Lock down the access model before agents inherit it — and prove it was clean at go-live.
The capabilities behind this outcome.
Security & compliance runs on the same platform — here's where to go deeper.
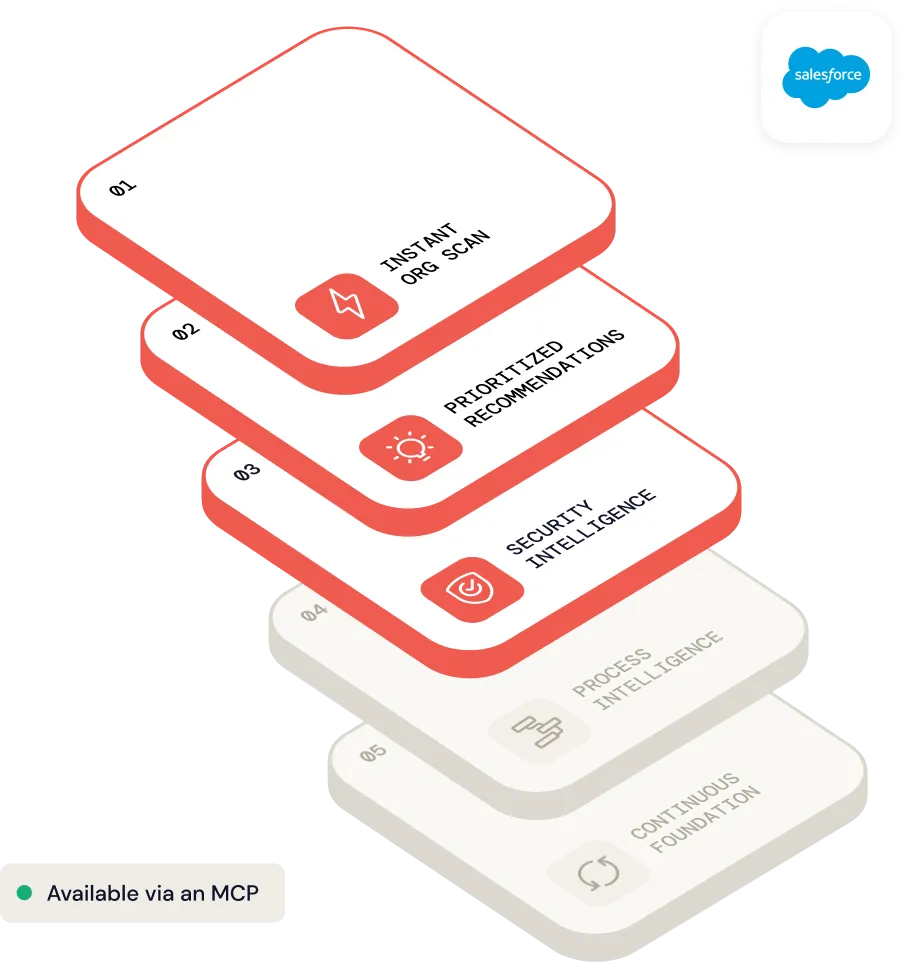
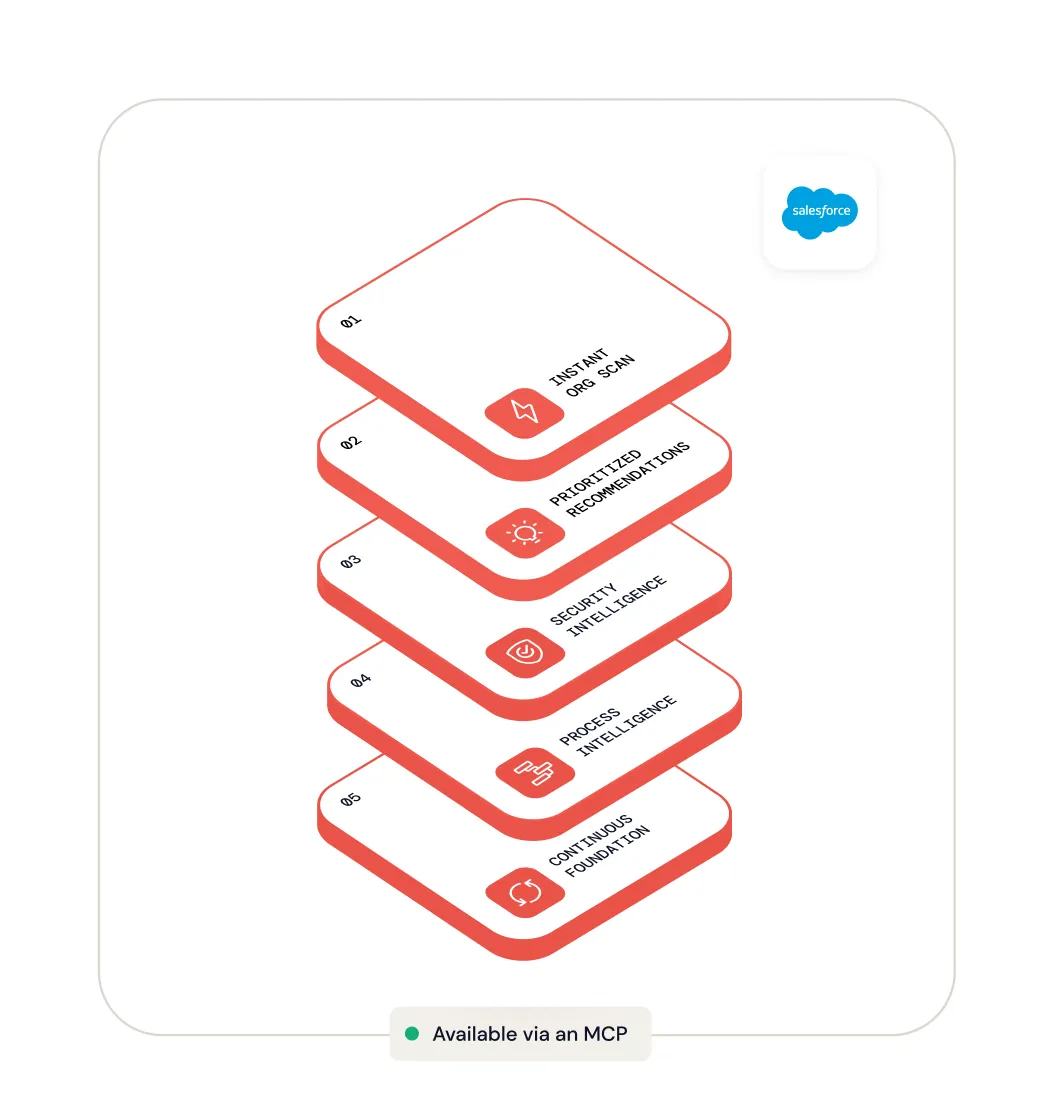
Security intelligence
Permissions, exposure, and the risky access paths hiding in your org — mapped and ranked.
Instant Org Scan
The two-minute X-ray that maps your whole org — the foundation this outcome is built on.
Org monitoring + AI readiness
Keep the org clean and secure as it evolves — and track drift over time.
Turn the lights on. Then, fix everything.
Scan your org in 2 minutes. See what's broken, in what order to fix it — and get the prompts to do the work.