IT & Security Leaders
Govern the access you can finally see.
Salesforce holds your most sensitive customer data, and the access map behind it grew one exception at a time. Hubbl reads your org's metadata, never its records, and shows you who can reach what, which integrations still hold keys, and what to close first. Then it keeps watching, so the fix holds.
Salesforce security debt accumulates quietly.
Nobody decides to over-permission an org. It happens one urgent request at a time: a profile cloned for a contractor, a permission set granted for a migration, an integration user created for a tool you retired two years ago. Each made sense on the day. Together they form an access map no one on your team can draw from memory, and that's the map an auditor, an attacker, or an AI agent will test first.
The access map, drawn from the org itself.
Hubbl scans profiles, permission sets, connected apps, and login activity and turns them into one view of who can reach what. No spreadsheets pieced together from exports, no waiting on an admin with a free week.
- Profiles & permission sets
Risky permissions flagged, with the users who hold them. - Connected apps & integrations
Every app with a door into the org, in one list. - Login activity
Who's using their access, and who hasn't logged in for months.
Risk ranked by what it could cost you.
Findings arrive prioritized by severity and mapped to Salesforce Well-Architected, so you can separate the public data exposure that needs attention today from the hygiene that can wait for next quarter.
- Severity-ranked findings
The exposures that matter most rise to the top. - Mapped to Well-Architected
Findings tied to the framework your auditors and architects already use. - Hubbl Score
One number for org health your board can follow.
From finding to fix without a six-week project.
Every recommendation carries the detail to act on it. Send it to Jira with the context attached, pass a low-risk change to an agent to make in Salesforce, or hand the backlog to a certified Hubbl partner.
- Jira-ready
Each finding becomes a ticket with the detail and impact attached. - Agent-ready
Prompts that do the work in Claude or Agentforce Vibes. - Partner delivery
Point a Hubbl partner straight at the high-priority items.
Stay clean between audits, not just before them.
Always-on scanning catches new findings as the org changes, so drift shows up as a line item, not a surprise. The trend becomes your evidence: exposure going down, quarter over quarter.
- Continuous scans
New high-severity findings flagged since the last scan. - Trend over time
The record you hand audit and the board. - Ready when audit asks
A current view of access, not last year's spreadsheet.
The same finding sounds different depending on who's in the room.
A scan result an admin hears as "more work on my plate" is the exact thing a CFO or COO hears as "we need this handled now." Hubbl gives you both versions of the finding — so your backlog stops being your private burden and becomes leadership's priority.
"That's more work for me."
One more thing on a list that's already too long — a risk you now own, on an org you're already stretched thin keeping alive.
"We need this now."
Quantified exposure, license waste, or an AI-readiness gap with a number attached — a business risk worth funding, resourcing, and prioritizing today.
Why it matters for you: the finding that feels like a burden at your altitude is a mandate at theirs. Hubbl translates the same issue into the language of the person who can give you the time, budget, or help to fix it — turning "I have too much to do" into "leadership asked me to lead this."
Every solution runs the same play.
No matter the role or the goal, Hubbl follows one motion — turn the lights on, understand and act, then stay clean and get AI-ready.
See the whole org
A credential-free X-ray in about two minutes — inventory, security exposure, and process reality no admin could map by hand.
Fix what matters first
A ranked backlog with the fix attached to every item — ticket it, prompt it, or delegate it, and close tech debt at the speed of AI.
Keep it healthy
Continuous monitoring holds the line as the org evolves — and turns your ongoing work into a health score you can show.
Lock down the foundation before you put agents on top of it.
Agentforce and AI assistants inherit whatever access your org already grants. An over-permissioned org is the biggest risk to put an agent on top of. Hubbl gives you the access map, the priorities, and the proof before the agents go live.
- Know who can see what - in minutes, not a quarter of manual review.
- Close findings your way - ticketed, automated, or delegated.
- Show your value - with a trend line, not a claim.
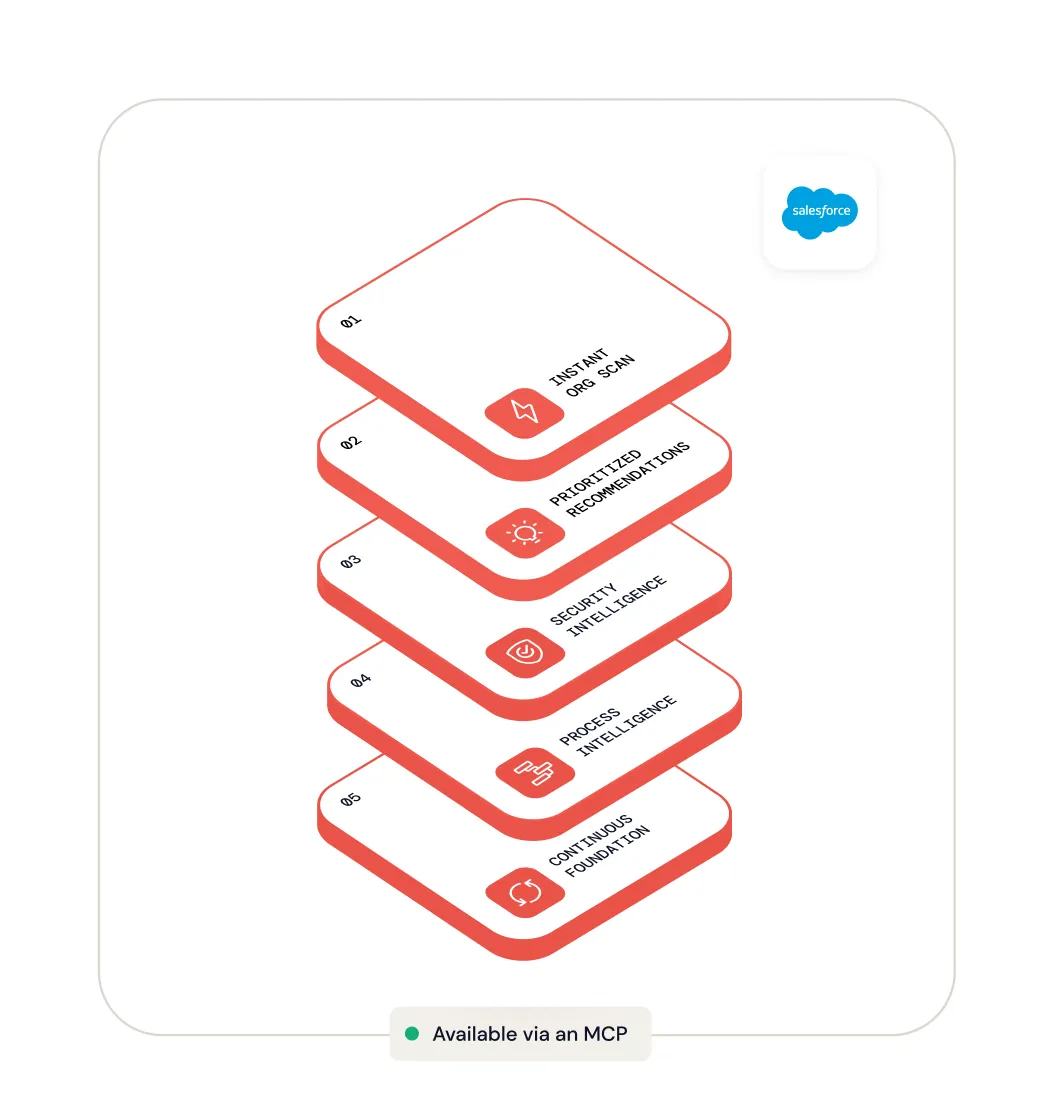
Hubbl is built for the leader who answers for the data.
Audit is coming
"I need to prove least privilege, not just claim it."
Get a current access map and a ranked list of what to close before the auditors ask.
You’re rolling out AI
"Security has to sign off on Agentforce."
See what an agent would inherit, and fix it before the pilot goes live.
You inherited the integrations
"I don't know which of these apps still has access."
Every connected app and integration user in one list, with login activity to show what's still live.
The capabilities behind your solution.
Same platform, pointed at your job. Here's where to go deeper.
Security Intelligence
Permissions, exposure, and risky access paths, ranked by severity.
Instant org Scan
The scan that maps your whole org, the foundation for everything above.
Data & Security
How the scan works: metadata only, read-only access, purged when done.
Turn the lights on. Then, fix everything.
Scan your org in 2 minutes. See what's broken, in what order to fix it — and get the prompts to do the work.